

EXCLUSIVE: Between 80,000 and 200,000 servers, company laptops and even private smartphones had been factory-reset inside hours throughout final week’s assault.

A cyber assault on the UK’s important nationwide infrastructure would have severe implications (Picture: Getty)
A harmful “wiper” assault on medical large Stryker has redefined the nightmare state of affairs for UK companies and the NHS, an skilled has warned – with Iranian-linked hackers now capable of remotely brick employees telephones and freeze life-saving provide chains on the contact of a button. The assault, launched on March 11 by the Handala group in retaliation for US-Israeli strikes on Iran, was no atypical ransomware demand.
Hackers compromised administrative credentials in Microsoft Intune – the device-management device trusted by 72% of enormous UK hospitals – and issued a world remote-wipe command. Between 80,000 and 200,000 servers, company laptops and even private smartphones had been factory-reset inside hours. Private photographs vanished, banking apps disappeared and eSIMs had been deleted, leaving staff unable to name emergency companies.
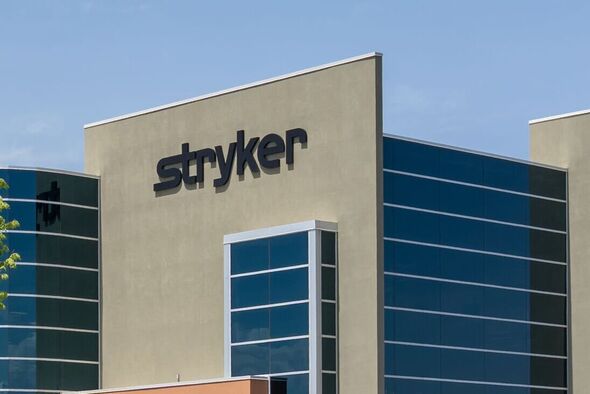
Stryker is the NHS’s major provider of defibrillators, surgical devices and orthopaedic implants (Picture: Getty)
As Stryker is the NHS’s major provider of defibrillators, surgical devices and orthopaedic implants, the “digital scorched earth” pressured the NHS Provide Chain to activate emergency demand-management protocols. Digital ordering programs collapsed, proving {that a} single cyber strike can now translate instantly into bodily threat on hospital wards.
SonicWall’s Government Vice President EMEA, Spencer Starkey, instructed Categorical.co.uk the incident marks a harmful evolution in state-aligned threats.
He defined: “SonicWall is observing a noticeable shift: sure state-aligned actors, notably these linked to geopolitical tensions, are prioritising disruption over monetisation. Wiper assaults are designed to destroy knowledge and halt operations reasonably than extract fee, aligning extra intently with strategic targets equivalent to signalling, retaliation, or destabilisation.
“That stated, this doesn’t characterize a wholesale alternative of ransomware, however reasonably an growth of the playbook. Financially motivated assaults nonetheless dominate general volumes; nevertheless, in periods of geopolitical escalation, harmful assaults are inclined to spike.”
Mr Starkey warned that UK companies at the moment are uncovered by regional companions and provide chains. He stated digital footprints can sign bodily threat, however single “purple flags” are hardly ever apparent in actual time.
He continued: “It’s tough to level to a single reside ‘purple flag’ in isolation and declare it predicts a selected occasion. These indicators usually solely grow to be clear in hindsight.
“What we do constantly observe, nevertheless, are patterns: sudden spikes or drops in assault visitors, botnet repositioning, and shifts in concentrating on behaviour that always cluster round geopolitical developments. When mixed with risk intelligence and timing, these patterns can act as early indicators that exercise is being staged or recalibrated.”
Healthcare and power sectors are most weak to oblique Iranian-linked threats, he added, citing advanced provide chains, legacy programs and excessive operational urgency that create harmful visibility gaps.
The rise of “Shadow AI” – staff feeding delicate knowledge into unauthorised instruments – additional complicates defence. Mr Starkey insisted AI-native safety is now important exactly due to this development.
The day’s largest headlines in UK and World information and extra Subscribe Invalid e mail
We use your sign-up to offer content material in methods you have consented to and to enhance our understanding of you. This will likely embody adverts from us and third events based mostly on our understanding. You possibly can unsubscribe at any time. Learn our Privateness Coverage
Russia: James Peddell discusses cyber assaults
He stated: “AI-native defence is changing into important exactly due to the rise of Shadow AI. Conventional safety fashions assume managed environments, however that assumption not holds.
“The trail ahead is to not remove Shadow AI totally, however to: acquire visibility into its utilization, apply real-time behavioural monitoring, use AI to detect anomalies at pace and scale. In different phrases, the identical know-how creating threat can also be changing into important to managing it.”
Assaults can begin in Center East places of work and leap to UK headquarters, with each collateral harm and bespoke lateral motion now evident.
Mr Starkey stated: “Each dynamics are evident. A major proportion of incidents nonetheless characterize collateral harm, with organisations impacted by way of shared vulnerabilities, platforms, or companions in affected areas. Nevertheless, there may be rising proof of extra tailor-made exercise, the place attackers perceive organisational constructions and try to maneuver laterally from regional places of work into international operations.
“This development factors to rising sophistication, notably in how attackers exploit belief relationships throughout geographies.”
Mr Starkey fears the Stryker precedent – weaponising administration instruments to wipe private units en masse – indicators the place threats are heading.
He stated: “The usage of administration instruments to wipe units is a powerful sign of the place threats could also be heading. The danger is not restricted to knowledge loss, however extends to operational paralysis at scale.
“For important nationwide infrastructure, the priority is much less about each system being wiped concurrently and extra about: lack of workforce performance, incapability to speak or coordinate, cascading operational disruption.
“So, whereas a full ‘digital scorched earth’ state of affairs continues to be an excessive case, the underlying functionality is actual, and it reinforces the necessity for stronger segmentation, entry controls, and resilience planning.”
Leave a Reply